By Joyce Ekeh
The Federal Government has moved to strengthen Nigeria’s digital defences, directing Ministries, Departments and Agencies (MDAs) to adopt the Domain Name System Security Extensions (DNSSEC) as part of efforts to protect government websites, prevent digital impersonation and secure critical online services.
The directive signals a renewed push to address weaknesses in Nigeria’s digital infrastructure, with the National Information Technology Development Agency (NITDA) announcing that DNSSEC compliance will form part of its cybersecurity assessment of government institutions.
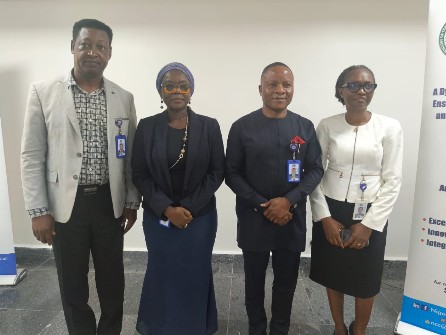
NITDA Director-General, Kashifu Inuwa Abdullahi, disclosed this at a cybersecurity awareness webinar organised by the Nigeria Internet Registration Association (NiRA) through its .ng Academy.
Represented by Mr Oluwasegun Falayan, Abdullahi said securing the Domain Name System (DNS) must become an integral part of Nigeria’s digital development strategy, warning that merely registering government domain names without protecting them leaves institutions exposed to avoidable cyber risks.
He stressed the need for government institutions to take the lead in securing their digital identities, particularly websites operating under the gov.ng domain.
“DNSSEC is a necessity at the point the country is,” he said, urging stakeholders to address the challenges limiting its adoption.
He further declared: “We must ensure that every .gov.ng is signed as much as possible, and we provide DNS as an inclusion in every security assessment that we do. It’s not enough to just have a domain; it must be secured and must be signed.”
The directive comes amid growing concerns over cyber threats targeting organisations and digital financial systems, raising questions about the resilience of public institutions increasingly dependent on online platforms for service delivery.
Why government websites need stronger protection
DNSSEC is a security technology designed to protect the internet’s Domain Name System by adding digital signatures to DNS records.
The technology allows internet systems to verify whether information directing users to a website is authentic and has not been maliciously altered.
Without adequate DNS protection, users could potentially be redirected to fraudulent websites designed to steal sensitive information, impersonate legitimate institutions or disrupt access to online services.
However, NiRA President, Mr Adesola Akinsanya, cautioned that adopting DNSSEC without the necessary technical expertise and proper configuration could create additional problems for organisations.
He warned that incorrect implementation could make websites inaccessible to users whose DNS resolvers validate digital signatures.
“Where DNSSEC is improperly configured, domains can become inaccessible to users whose resolvers validate signatures. Our priority must therefore be competence, coordination and careful implementation, rather than adoption for its own sake,” Akinsanya said.
He also clarified that DNSSEC should not be mistaken for a complete cybersecurity solution, noting that it does not encrypt internet traffic, prevent traffic-flooding attacks or protect against compromised registrar credentials.
“It is an important layer of security, but it must work alongside other protective measures to create a resilient digital ecosystem,” he said.
Nigeria faces mounting cyber and financial risks
Akinsanya cited figures from Check Point indicating that the average Nigerian organisation faced approximately 4,361 attempted cyberattacks weekly in June, compared with a global average of about 2,270.
He also referenced Nigeria Inter-Bank Settlement System figures showing that digital-payment fraud reached ₦25.85 billion in 2025.
The figures, he argued, demonstrate the growing financial implications of weak digital security and the need for organisations to treat cybersecurity as an economic priority rather than merely a technical responsibility.
“DNS security is not a technical hobby. It is an economic question,” he said.
Akinsanya urged government institutions and other organisations to review access to their domain accounts, establish clear administrative controls and activate multi-factor authentication to reduce the risk of unauthorised access.
He explained that although NiRA manages Nigeria’s .ng domain registry, individual organisations remain responsible for the security of their DNS configurations and registrar accounts.
He also cautioned against allowing the drive to expand Nigeria’s internet domain space to overshadow the need for security.
While NiRA is targeting a 30 per cent expansion of the .ng namespace, he insisted that growth must be accompanied by reliability and proper protection.
“I am not asking for more domains for their own sake. A .ng that is unsafe or unreliable is worse than none,” he said.
Experts seek critical infrastructure status for DNSSEC
Adding to the debate, the Head of Incident Handling at the Nigeria Computer Emergency Response Team, Daniel Onyekpeze, proposed that DNSSEC be accorded Critical National Information Infrastructure status and adopted across different sectors.
The proposal reflects growing recognition that the security of internet addressing systems is central to the protection of government services, financial transactions, businesses and other essential digital operations.
Participants at the webinar called on organisations to integrate DNSSEC into broader cybersecurity frameworks, stressing that protecting digital infrastructure requires sustained investment, technical competence and cooperation among government agencies, internet operators and other stakeholders.
For the Federal Government, the challenge now extends beyond issuing a directive. Ensuring that MDAs implement DNSSEC correctly, maintain secure domain accounts and strengthen other layers of cybersecurity will be critical to protecting public digital services.
As Nigeria accelerates its digital transformation, the security of government websites is increasingly becoming an issue of public trust, economic stability and national security.